
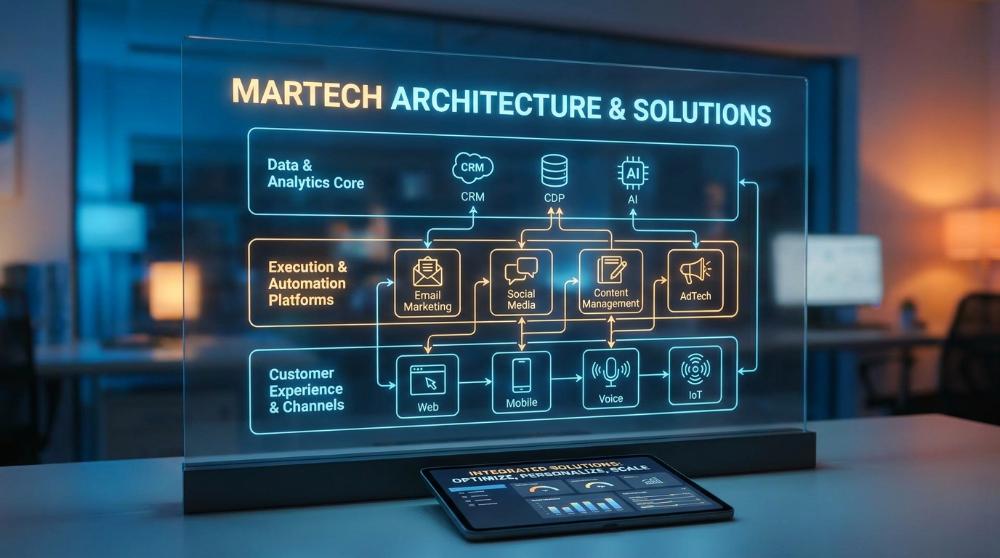
Authorship & Editorial Verification: Written by Ramadhani, informed by enterprise martech architecture practice and implementation patterns observed across web, app, CRM, CDP, advertising, and BI integrations. The editorial process prioritizes source-grounded claims, explicit architectural trade-offs, and verification against the evidence supplied in the brief; no unverified metrics or vendor claims are introduced.
Marketing technology is the operating system for customer data, orchestration, activation, and measurement. Enterprise teams build scalable martech solutions by enforcing a canonical event model, identity rules, consent propagation, and governance before tool selection. According to Salesforce’s 2023 State of Marketing report, 84% of B2B marketers say attribution is important, but only 37% fully use it in decisions.
| Decision Area | What It Means in Practice | Enterprise Requirement | Common Trade-off | Risk if Mishandled |
|---|---|---|---|---|
| Core Definition | Marketing technology is the architecture that connects data capture, identity, orchestration, activation, and measurement across channels | Treat it as a system design problem, not a tool list | Broader scope increases governance complexity | Fragmented execution and inconsistent customer views |
| Primary Architecture Layers | Data capture, identity resolution, orchestration, activation, measurement, governance | Define interfaces between layers before procurement | More explicit design reduces tool flexibility in the short term | Broken attribution and duplicate audiences |
| Geography | Global enterprise markets, with practical relevance for APAC, EMEA, and North America | Support multi-region operating models and data residency expectations | Regional variation increases implementation complexity | Cross-border transfer failures and local compliance gaps |
| Compliance and Standards | GDPR, Indonesia UU PDP, CCPA/CPRA and other U.S. state privacy laws where applicable; ISO/IEC 27001 and SOC 2-aligned controls | Build consent, retention, and access control into the stack | Stronger controls can slow activation velocity | Privacy breaches and audit findings |
| Vertical Specialism | B2B SaaS, eCommerce, financial services, education, healthcare, and multi-brand consumer businesses | Support lifecycle marketing, lead management, personalization, and attribution | Vertical-specific rules increase configuration overhead | Incompatible journeys and weak measurement fidelity |
| Organization Size Fit | Mid-market to enterprise organizations with multiple business units, regions, channels, or marketing operations teams | Establish ownership for taxonomy, consent state, and lifecycle orchestration | More stakeholders lengthen decision cycles | Unclear accountability and tool sprawl |
| Tooling Strategy | Use digital marketing tools as components inside a governed architecture | Standardize event schemas and integration contracts | Faster point solutions can create hidden integration debt | Duplicate data pipelines and QA failures |
| Stack Economics | Cost is driven as much by integration and governance as by licenses | Budget for schema management, QA, and identity stitching | Higher upfront architecture work can delay launch | License underutilization and poor ROI visibility |
| Operating Model | Explicit ownership for taxonomy, consent, and measurement logic | Separate platform administration from data governance | Requires stronger cross-functional coordination | Trigger drift, audience inflation, and unstable reporting |
| Strategic Outcome | Scalable personalization, reliable attribution, and controlled activation | Align channels to one customer-data logic | Optimization depends on disciplined enforcement | Over-automation, unsubscribe growth, and lower incremental conversion |
This matters most in global enterprise markets, with practical relevance for APAC, EMEA, and North America, especially where customer data crosses jurisdictions. The compliance profile includes GDPR, Indonesia’s UU PDP, and U.S. state privacy laws such as CCPA/CPRA where applicable, alongside ISO/IEC 27001 and SOC 2-aligned controls. The most relevant use cases are B2B SaaS, eCommerce, financial services, education, healthcare, and multi-brand consumer businesses, typically at the mid-market to enterprise level where multiple business units, regions, channels, and marketing operations teams must share one operating model without losing governance or measurement integrity.
What is marketing technology architecture, and how do the core layers—data capture, identity resolution, orchestration, activation, measurement, and governance—fit together in an enterprise stack?
Marketing technology architecture is the operating model that connects customer data, identity rules, journey logic, channel activation, measurement, and governance into one controlled system. In enterprise marketing technology, the stack only works when those layers share a canonical event model, explicit data contracts, and a single source of truth for consent and audience state.
In practical enterprise design, the data capture layer ingests web, app, CRM, product, offline, and ad-platform events into a canonical schema. Identity resolution then stitches those events into a person or account profile using deterministic and governed probabilistic rules, so downstream activation does not fragment the same customer into multiple audiences. Orchestration applies lifecycle logic, suppression rules, and trigger sequencing across channels, while activation publishes segments to email, paid media, SMS, sales tools, and on-site personalization. Measurement closes the loop through attribution, experimentation, and incrementality analysis, but only if event taxonomy, conversion definitions, and timestamp handling are consistent across systems.

The hidden failure point is usually not the martech tool itself but the integration and governance layer surrounding it: event schema management, consent propagation, identity stitching, and QA across web, app, CRM, CDP, ad platforms, and BI. Ramadhani’s architecture-first heuristic is to treat each additional source system as multiplying failure points unless the canonical event model is enforced; otherwise, one extra connector can create duplicate audiences, broken suppression, and inflated reach estimates. This is especially relevant for global enterprise teams operating across APAC, EMEA, and North America, where GDPR, Indonesia’s UU PDP, and U.S. state privacy laws affect consent retention, data minimization, and cross-border transfer design.
Governance is therefore not a final layer; it is the control plane. It defines ownership for taxonomy, consent state, lifecycle orchestration, retention, and access control, which is why scalable marketing technology solutions require more than tool administration. According to Salesforce’s 2023 State of Marketing report, 84% of B2B marketers say attribution is important, but only 37% say they fully use it in decision-making. That gap usually reflects architectural inconsistency, not analytics intent. According to Gartner’s 2023 marketing analytics coverage, 63% of marketing leaders prioritize improving data quality and accessibility. That priority is justified because measurement quality depends on upstream discipline, not downstream dashboards.
What are the typical costs, ROI drivers, and performance benchmarks for building a scalable martech stack, including integration overhead, license utilization, and conversion lift?
The true cost of marketing technology is rarely the license fee alone; it is the ongoing expense of integration labor, data governance, identity stitching, QA, and measurement maintenance. In enterprise stacks, ROI is usually created when those hidden costs are controlled and activation decisions improve conversion quality, not just campaign volume.
According to Gartner’s 2023 marketing analytics survey coverage, 63% of marketing leaders say improving data quality and accessibility is a top priority for marketing analytics. That priority reflects a practical economic reality: if data is incomplete, late, or inconsistent, license utilization falls, audiences fragment, and attribution confidence deteriorates. In other words, the economic center of marketing technology is the data layer, not the tool count.

A useful budgeting model separates costs into four buckets: platform licenses, integration overhead, operating governance, and optimization labor. Integration overhead typically grows fastest when each new source system introduces a custom event schema, consent mapping, and test suite. In enterprise practice, the hidden cost is often not the software itself but the work required to keep web, app, CRM, CDP, ad platforms, and BI aligned to a canonical event model. That is why digital marketing solutions should be evaluated as an architecture problem, not a procurement checklist.
The most reliable ROI drivers are license utilization, audience quality, and conversion lift. License utilization improves when dormant seats, unused modules, and overlapping capabilities are removed from the stack. Conversion lift becomes credible only when identity resolution and trigger logic are validated before scale-up; otherwise, duplicate suppression errors can inflate reach estimates and distort reported performance. Counter-intuitively, more automation can reduce returns if trigger frequency is not bounded, because excessive real-time messaging often increases unsubscribes and lowers incremental conversion after a threshold.
Scott Brinker’s 2024 martech analysis notes, “The most important trend in martech is not more tools, but better integration of tools around customer data and journeys.” That principle is also the clearest benchmark: a scalable stack should reduce manual reconciliation, preserve a single audience truth, and improve decision latency across marketing technology operations.
For teams comparing digital marketing solutions against broader digital marketing resources, the benchmark is not category breadth but whether the stack measurably reduces schema drift, attribution disputes, and wasted activation spend.
How do enterprise teams implement marketing technology without creating data silos, broken attribution, duplicate audiences, or privacy/compliance failures, and what are the most common failure modes?
Enterprise teams avoid martech failure by enforcing a canonical event model, explicit identity rules, consent-state propagation, and governed activation sequencing before scale-up. The main risks are not tool count alone, but unmanaged schema drift, audience duplication, attribution gaps, and privacy violations across web, app, CRM, CDP, ad platforms, and BI.
The practical control point is the data contract: every source system should emit events with defined names, required properties, ownership, and validation rules. Without that layer, each additional source multiplies failure points, especially when teams stitch identity after audiences are already active. In those conditions, duplicate suppression breaks, reach estimates inflate, and attribution becomes internally inconsistent because one user can be represented by multiple records across systems. Ramadhani’s architecture-first approach is to define the data layer, identity resolution logic, and measurement standards before enabling activation tools, because channel execution can otherwise outrun governance.

What prevents data silos in enterprise marketing technology?
Data silos are prevented by centralizing taxonomy governance, not by merely connecting tools. A scalable marketing technology operating model assigns clear ownership for event naming, consent state, and lifecycle orchestration, then requires every platform to conform to the same schema and identity rules. This is especially important in digital marketing solutions environments where web, mobile, CRM, and advertising systems all generate overlapping customer signals.
In practice, teams should treat event schema management as a controlled change process: new events, properties, and lifecycle states should be versioned, reviewed, and tested before deployment. That reduces the hidden integration and governance cost that typically exceeds the platform license itself. It also improves downstream measurement because BI, CDP, and activation layers all read from the same canonical definitions instead of reconciling competing versions of “lead,” “qualified lead,” or “customer.”
Why do attribution and audience duplication break so often?
Attribution and audience duplication break when identity stitching happens after activation rather than before it. If a customer appears as separate identities across devices or channels, the system may count them twice, suppress them incorrectly, or assign conversion credit to the wrong touchpoint. This is a common failure mode in marketing management software stacks that prioritize channel launch speed over identity integrity.
The operational fix is to resolve identity rules early, define deterministic and probabilistic matching logic explicitly, and validate those rules against expected suppression and conversion paths before audiences are activated. Otherwise, teams often publish inflated audience sizes and understate overlap across campaigns, which distorts both spend allocation and performance reporting.
What privacy and compliance controls matter most?
Privacy and compliance failures are usually caused by weak consent propagation and retention controls, not by the mere presence of more tools. For global enterprise markets, the stack must support GDPR, Indonesia’s UU PDP, applicable U.S. state privacy laws such as CCPA/CPRA, and platform advertising policy constraints. That means consent must travel with the user record, retention rules must be enforceable at the data layer, and cross-border transfers must be governed consistently across APAC, EMEA, and North American operations.
The most robust implementations align marketing technology with security and governance frameworks such as ISO/IEC 27001 and SOC 2-style controls. In practice, this means access control, auditability, approved data retention windows, and documented lawful basis for processing. For sectors such as B2B SaaS, eCommerce, financial services, education, healthcare, and multi-brand consumer businesses, these controls are not optional because lifecycle marketing and attribution depend on continuous data movement across jurisdictions.
A useful operating rule is simple: if consent state, identity state, and event schema are not all auditable, the stack is not ready for broad activation.
How does a composable martech architecture compare with a suite-based or all-in-one platform approach in terms of flexibility, time-to-value, total cost of ownership, and governance trade-offs?
Composable martech architecture usually delivers the highest flexibility and the best fit for enterprise-grade governance, but only when the team can enforce canonical event models, identity rules, and data contracts. Suite-based or all-in-one platforms typically reduce initial coordination cost and time-to-value, yet they often trade away depth of control, cross-system extensibility, and long-term architectural precision in complex marketing technology environments.
In practice, the decision is less about whether a platform “integrates” and more about where complexity is absorbed: inside one vendor’s opinionated model or across a governed integration layer that your team controls. As Ann Handley notes, “Data-driven marketing is not just about collecting data; it is about turning data into decisions and decisions into action at scale.” That distinction matters because the governance burden in marketing technology does not disappear in a suite; it is simply relocated into vendor constraints, configuration limits, and downstream workarounds.
| Evaluation criterion | Composable architecture | Suite-based / all-in-one platform |
|---|---|---|
| Flexibility | Highest, because each layer can be replaced independently | Moderate to low, because modules share the same vendor model |
| Time-to-value | Slower initial setup due to orchestration and integration design | Faster initial deployment when default workflows match requirements |
| Total cost of ownership | Can be lower or higher depending on integration, QA, and governance load | Often simpler to budget at procurement time, but hidden costs emerge in customization and lock-in |
| Identity and consent governance | Strong when canonical identity, consent state, and event taxonomy are centrally enforced | Easier to start, but governance can become opaque across bundled modules |
| Measurement quality | Better control over attribution logic, but requires disciplined data contracts | Convenient reporting, but more likely to inherit vendor-defined limitations |
| Change management | More modular and resilient to replacement | Faster for standardized use cases, harder to remodel deeply |
For organizations that need broad standardization with limited internal MarTech architecture capacity, a suite can be appropriate. For enterprises with multiple regions, business units, or regulated data flows, composability usually wins once the stack must support digital marketing solutions across CRM, CDP, analytics, ad activation, and compliance controls. It also aligns better with marketing agency software environments where multi-client governance and segmentation logic must remain isolated. In more generalized operating models, teams should still evaluate digital marketing solutions against their required state of identity stitching, consent propagation, and measurement integrity rather than against feature count alone. A well-governed stack of digital marketing tools can outperform a monolithic suite when the architecture is explicit and the operating model is mature.
What regulatory, security, and regional constraints affect marketing technology implementations across GDPR, U.S. state privacy laws, and Indonesia’s UU PDP, especially for consent, data retention, and cross-border transfers?
Marketing technology implementations across GDPR, U.S. state privacy laws, and Indonesia’s UU PDP are constrained by consent governance, retention limits, purpose limitation, and cross-border transfer controls. The practical requirement is to make policy state machine-readable across capture, identity, activation, and deletion workflows so every audience, event, and export path remains legally auditable.
These constraints apply to global enterprise markets, with practical relevance for APAC, EMEA, and North American operating environments, especially for organizations managing multi-jurisdictional customer data. In regulated stacks, security and compliance should be treated as architecture inputs, not legal afterthoughts. That means consent state must propagate from web and app collection into CRM, CDP, ad platforms, and BI layers; retention rules must be enforced at the record and event level; and cross-border transfers must be mapped to approved processing locations and contractual controls. This is particularly material for B2B SaaS, eCommerce, financial services, education, healthcare, and multi-brand consumer businesses that rely on lifecycle marketing, lead management, personalization, and attribution. For mid-market to enterprise organizations with multiple business units, regions, channels, or marketing operations teams, the governance burden rises as soon as one stack serves multiple regimes.
According to Scott Brinker’s 2024 martech landscape analysis, the average organization uses 111 martech tools. At that scale, the dominant failure mode is not tool scarcity but control-plane fragmentation: one system stores consent, another stores audience membership, and a third executes suppression logic that no longer matches the source of truth. Ramadhani’s field heuristic applies directly here: every additional source system multiplies failure points unless a canonical event model and data contract are enforced. In practice, that means defining consent artifacts, event taxonomy, identity stitching rules, retention clocks, and deletion propagation before enabling activation in digital marketing solutions.
Common controls include ISO/IEC 27001-aligned security governance, SOC 2-aligned access and change management, and auditable vendor risk reviews. Under GDPR, organizations need a lawful basis, minimization, and transfer safeguards; under U.S. state privacy laws, they need notice, opt-out handling, and category-specific processing discipline; under Indonesia’s UU PDP, they need lawful processing, retention discipline, and cross-border handling that is operationally documented. The most reliable operating model centralizes consent and identity logic, while allowing channel teams to execute only through governed templates, suppressed cohorts, and approved exports supported by digital marketing resources. For teams evaluating digital marketing solutions, the compliance design should be validated alongside attribution, audience design, and deletion workflows.
Practical Implementation, Edge Cases, and Failure Modes
A scalable martech implementation should start with a canonical event model, explicit identity rules, consent-state propagation, and measurement logic before any audience activation begins. In enterprise environments, the main risk is not tool selection alone; it is uncontrolled schema drift, duplicate profiles, and misfired orchestration across web, app, CRM, CDP, ad, and BI layers.
How should enterprise teams implement martech without creating silos?
Enterprise teams should implement martech as a governed data product, not as disconnected channel tooling. The practical sequence is: define the canonical event taxonomy, map source-system fields to shared contracts, establish identity stitching rules, propagate consent status across systems, and validate activation logic in a controlled environment before production scale.
This sequence matters because each additional source system multiplies failure points unless the stack is anchored to a canonical event model and enforceable data contracts. In practice, the data layer should specify event names, required attributes, timestamp logic, and identity keys before any downstream audience or journey logic is enabled. That prevents one team from building on top of incompatible definitions created by another.
A robust operating model usually assigns explicit ownership for three domains:
- Taxonomy ownership: who defines and approves event names, traits, and lifecycle stages.
- Consent ownership: who governs opt-in state, retention rules, and jurisdiction-specific processing.
- Orchestration ownership: who decides trigger frequency, suppression rules, and journey exit conditions.
Without these assignments, teams often optimize local channel performance while degrading the system as a whole.
What is the most common martech failure mode in enterprise activation?
The most common failure mode is premature activation: teams launch audiences before identity rules and data quality checks are complete. That produces duplicate suppression errors, inflated reach estimates, and inconsistent attribution because the same person may exist under multiple identifiers across CRM, CDP, web analytics, and ad platforms.
A related failure mode is over-automation. If trigger frequency is not bounded, real-time messaging can become excessive, causing unsubscribes to rise and incremental conversion to decline after a certain threshold. The operational issue is not automation itself; it is the absence of frequency governance, suppression logic, and lifecycle sensitivity.
Another recurring problem is broken attribution caused by partial instrumentation. If web events, app events, CRM updates, and conversion responses are not aligned to the same identity and event model, then the measurement layer will reconcile inconsistent journeys and produce misleading channel credit.
How should teams handle identity resolution and consent propagation?
Identity resolution should be treated as a rules engine with documented precedence, not as an afterthought inside a vendor UI. Teams need deterministic matching rules where possible, clear merge logic for anonymous-to-known transitions, and a formal process for handling collisions, stale records, and cross-device ambiguity.
Consent propagation must be designed to travel with the customer record and the event stream. If consent exists only in one system, downstream channels can remain out of compliance or suppress eligible users incorrectly. For multi-jurisdictional organizations, this becomes especially important across regions with different consent and retention requirements, including GDPR, Indonesia’s UU PDP, and applicable U.S. state privacy laws.
Operationally, the safest pattern is to:
1. Store consent state in a governed source of truth.
2. Replicate it into activation systems with auditability.
3. Enforce suppression before message dispatch.
4. Version consent logic by jurisdiction when rules differ.
How do you prevent duplicate audiences and broken attribution?
Duplicate audiences usually emerge when identity stitching is incomplete or when segmentation rules are built from inconsistent field definitions across tools. To prevent this, segment logic should reference a canonical customer profile, not separate local copies of the same person in each platform.
Broken attribution is typically a measurement governance problem. The organization must define which touchpoints count, how conversions are deduplicated, and how offline and online events are joined. According to Salesforce’s 2023 State of Marketing report, 84% of B2B marketers say attribution is important for their organization, but only 37% say they are fully using attribution in decision-making. That gap usually reflects executional inconsistency, not lack of analytic intent.
A practical control set includes:
- shared event definitions across systems,
- stable campaign identifiers,
- a single conversion taxonomy,
- deduplication rules for repeat events,
- and QA checks before every campaign launch.
What operational controls reduce hidden integration overhead?
The hidden cost in martech is often integration and governance, not license spend. The most effective controls are data contracts, automated QA, and schema versioning. A data contract defines what each source system must send, in what format, and with which required fields. Schema versioning prevents silent breakage when teams change event payloads without notifying downstream consumers.
Additional controls include:
- automated validation of required fields,
- anomaly detection for event volume drops or spikes,
- reconciliation between source and destination counts,
- and documented rollback procedures for failed releases.
This is especially important in enterprise programs that span web, app, CRM, CDP, ad platforms, and BI. Without these controls, every new source system increases operational fragility instead of expanding capability.
How should teams compare composable, suite-based, and all-in-one architectures?
The right architecture depends on how much flexibility the organization needs versus how much governance it can support. Composable architectures offer greater control and better fit for complex enterprise environments, but they require stronger orchestration and more disciplined ownership. Suite-based and all-in-one platforms reduce coordination effort but can constrain data models, workflow customization, and jurisdiction-specific policy enforcement.
| Architecture model | Strengths | Constraints | Best fit |
|---|---|---|---|
| Composable | High flexibility, modular replacement, stronger fit for custom event and identity logic | Higher integration and governance burden | Multi-brand, multi-region, data-mature enterprises |
| Suite-based | More unified vendor operations, fewer moving parts | Less flexibility around specific workflows and data contracts | Organizations prioritizing standardization over customization |
| All-in-one | Fast initial deployment, simpler administration | Risk of rigid architecture and limited specialization | Smaller teams with lower complexity and fewer jurisdictions |
What regulatory and regional constraints matter most?
Marketing technology implementations must account for regional privacy and security obligations from the start, especially in global operating environments. GDPR, Indonesia’s UU PDP, and applicable U.S. state privacy laws can affect consent collection, retention windows, lawful basis handling, and cross-border data transfers. Platform advertising policies and security controls also shape what can be activated and how it is audited.
For enterprises operating across APAC, EMEA, and North America, the compliance model should distinguish between:
- data collection rules,
- processing permissions,
- retention and deletion requirements,
- transfer restrictions,
- and user rights handling.
Security governance should align with commonly used control frameworks such as ISO/IEC 27001 and SOC 2-aligned practices. The practical implication is that martech architecture must support policy enforcement, not just campaign execution.
What are the most important boundary conditions for enterprise scale?
The most important boundary conditions are organizational, not just technical. MarTech scales reliably only when the business can support clear ownership, disciplined change management, and a shared measurement framework across regions and business units. Mid-market and enterprise organizations with multiple teams, channels, or markets are the ones most likely to need this structure.
Industry context also matters. B2B SaaS, eCommerce, financial services, education, healthcare, and multi-brand consumer businesses typically depend on lifecycle marketing, lead management, personalization, and attribution. Those use cases become fragile when teams move faster than governance. Ramadhani’s architecture-first principle applies here: define the data layer, identity rules, and measurement logic before selecting activation tools, so channel execution does not outrun governance.
Frequently Asked Questions (FAQ)
What is the first thing an enterprise should define before buying martech tools?
The first thing to define is the canonical data and event model. That includes event names, required attributes, identity keys, and consent-state rules. If those are undefined, every tool will interpret customer data differently, which creates duplicate audiences, broken attribution, and expensive rework after deployment.
Why do martech implementations fail even when the tools are good?
They fail because the operating model is weak. Common causes include incomplete identity stitching, uncontrolled schema changes, missing consent propagation, and campaign activation before QA. Tool quality does not compensate for poor governance, especially when multiple systems exchange events, profiles, and audience segments across regions.
How does over-automation reduce marketing performance?
Over-automation can increase message frequency beyond what customers tolerate. When trigger volume is not bounded, users may receive too many real-time messages, which raises unsubscribes and can lower incremental conversion. The issue is not automation itself; it is the absence of frequency caps, suppression logic, and lifecycle controls.
What is the biggest hidden cost in a scalable martech stack?
The biggest hidden cost is usually the integration and governance layer, not the license fee. Event schema management, identity resolution, consent propagation, and QA across web, app, CRM, CDP, ad platforms, and BI create ongoing operational cost. Without data contracts and validation, complexity compounds with each added system.

About the Author
admin
Contributing writer and researcher exploring modern digital architecture, search visibility, and minimalist systems.
2 Responses